PhiloCyber / Open tool / Model
Threat modeling, done by a pipeline of specialist agents.
Point it at an RFC or an architecture description. Seven specialist agents run STRIDE, PASTA and attack-tree analysis, debate the findings Red vs Blue, and hand back a prioritized threat register with an evidence trail. Local-first: every project is a folder you control.
- Status
- In development
- Version
- v0.1.0
- Licence
- Not public yet
- Repository
- Not public yet
The problem
Ask a single model to threat-model a system and you get one pass, one perspective and no evidence trail — findings nobody can verify, prioritize or defend in front of a reviewer. What makes a threat model credible is the triangulation, the challenge and the traceability, and that is exactly the part a chat window does not do.
Who it is for
Security and AppSec teams reviewing architectures, engineers who need a defensible threat model before production, and reviewers who want to disagree with a finding instead of re-deriving it.
What it does
Three methodologies, triangulated
STRIDE, PASTA and attack-tree analysts run as separate specialist agents — in hybrid, parallel or cascade mode — instead of one model's single pass.
Adversarial review built in
A Red/Blue team debate challenges every candidate threat, then a DREAD validator calibrates scores against the official grid.
Evidence-gated priorities
High and critical priorities demand traceable evidence: components, trust boundaries, endpoints and security configs.
Grounded in a real corpus
RAG over OWASP Top 10, OWASP API and AI Security, NIST AI RMF, MITRE ATT&CK and CAPEC — plus your own project documents.
Local-first and offline-capable
Every project is a portable folder with its own SQLite database. Runs fully offline with Ollama, or plugs into Gemini, Kimi or AWS Bedrock.
It learns from your reviews
Confirm/Reject decisions feed back as few-shot examples on the next run, and run diffs show what changed between analyses of the same system.
How it works
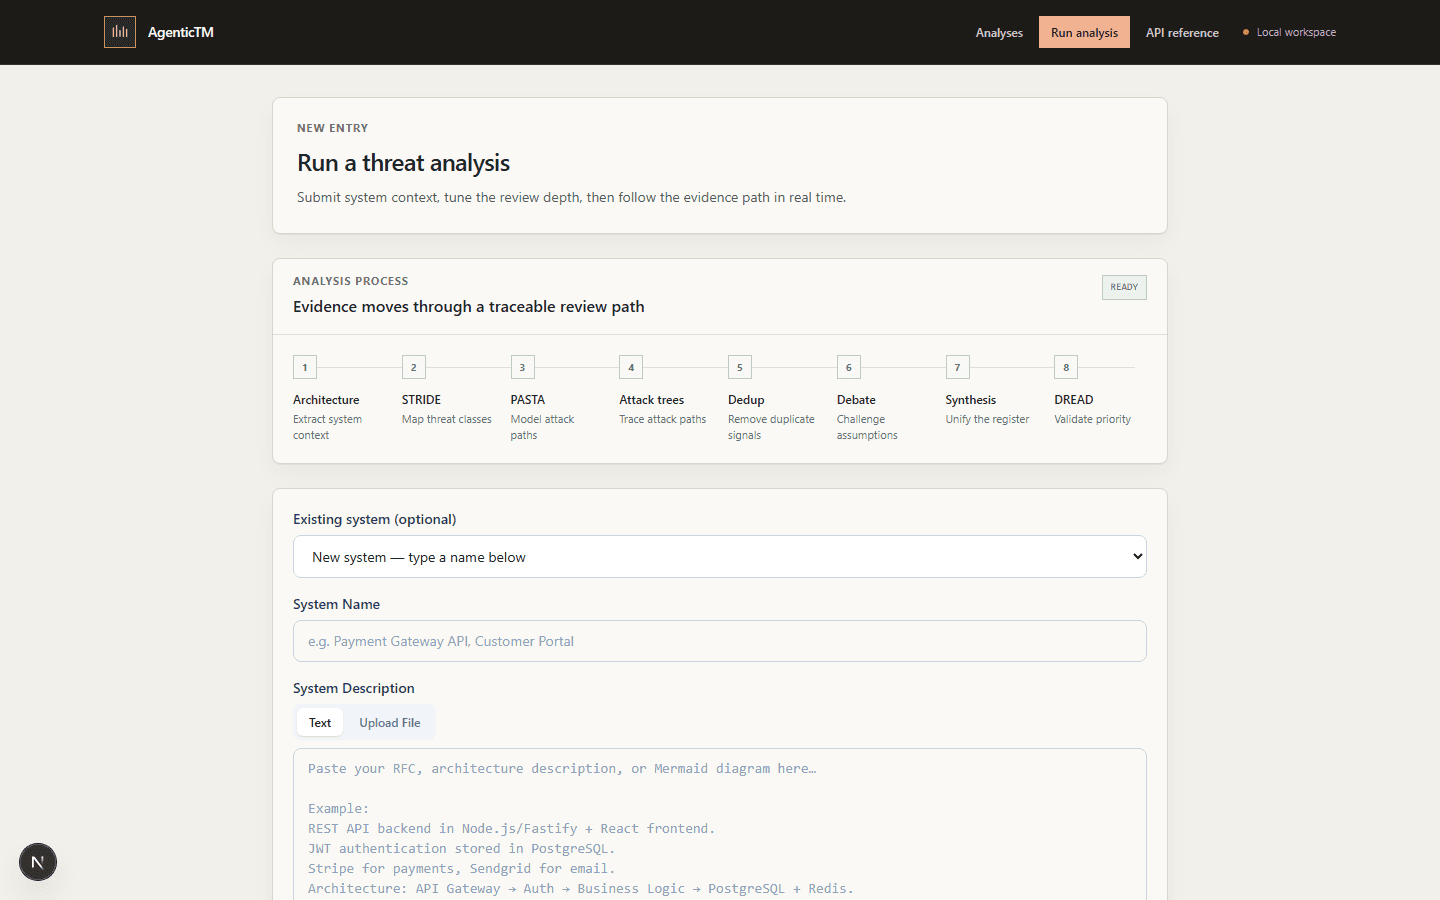
- 01/08Architecture Parser
Extracts components, data flows and trust boundaries from your RFC, and draws the DFD and architecture diagrams.
- 02/08STRIDE Analyst
Maps threat classes against each element of the system.
- 03/08PASTA Analyst
Runs the seven-stage risk analysis over the attack surface.
- 04/08Attack Tree Analyst
Traces concrete attack paths instead of generic checklist items.
- 05/08Pre-dedup
Merges duplicate findings with embeddings and a confidence filter, keeping each methodology's fields.
- 06/08Red/Blue Debate
Red argues, Blue answers, a judge can rule — rounds stop early on convergence.
- 07/08Threat Synthesizer
Unifies everything into one register: unique IDs, OWASP mapping, NIST/CIS control references, evidence sources.
- 08/08DREAD Validator
Calibrates scores against the official DREAD grid and rewrites each threat from the adversary's perspective.
Interface
What it looks like in practice
Captures from the current build. The interface is still moving, so expect changes before the first public release.
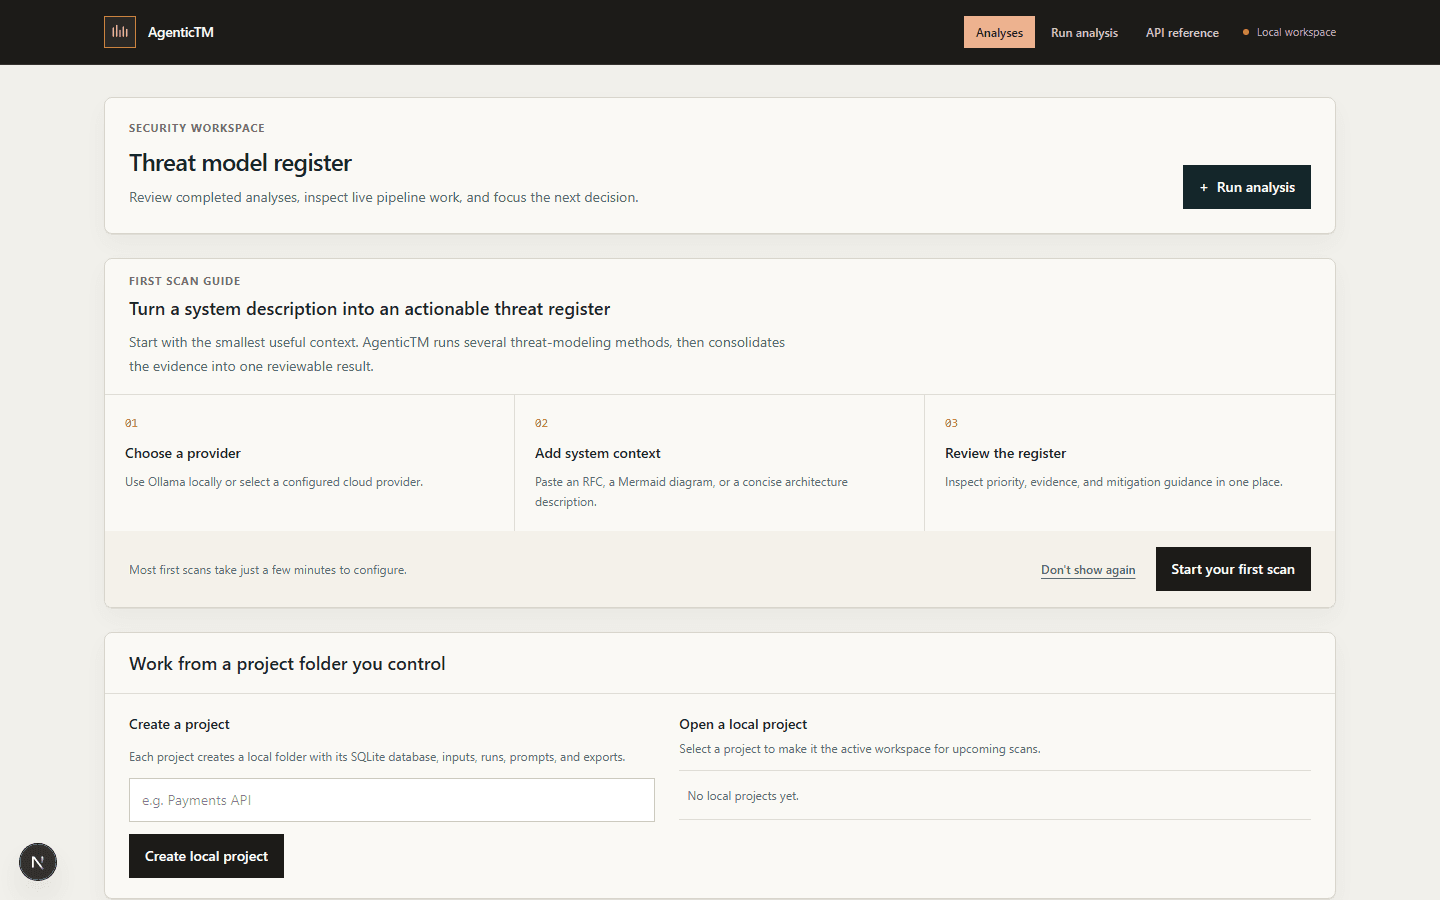
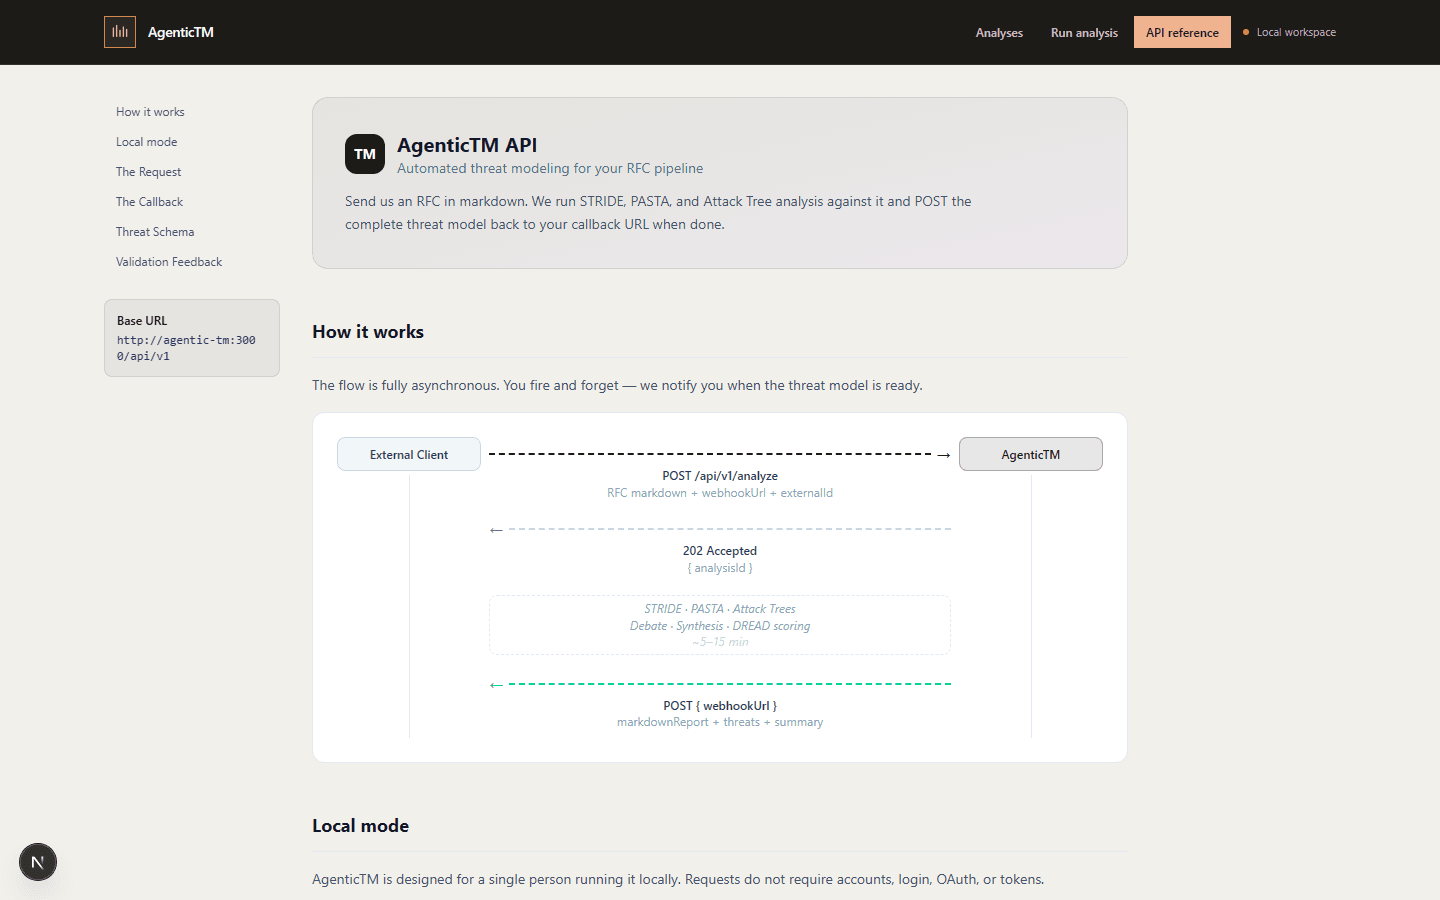
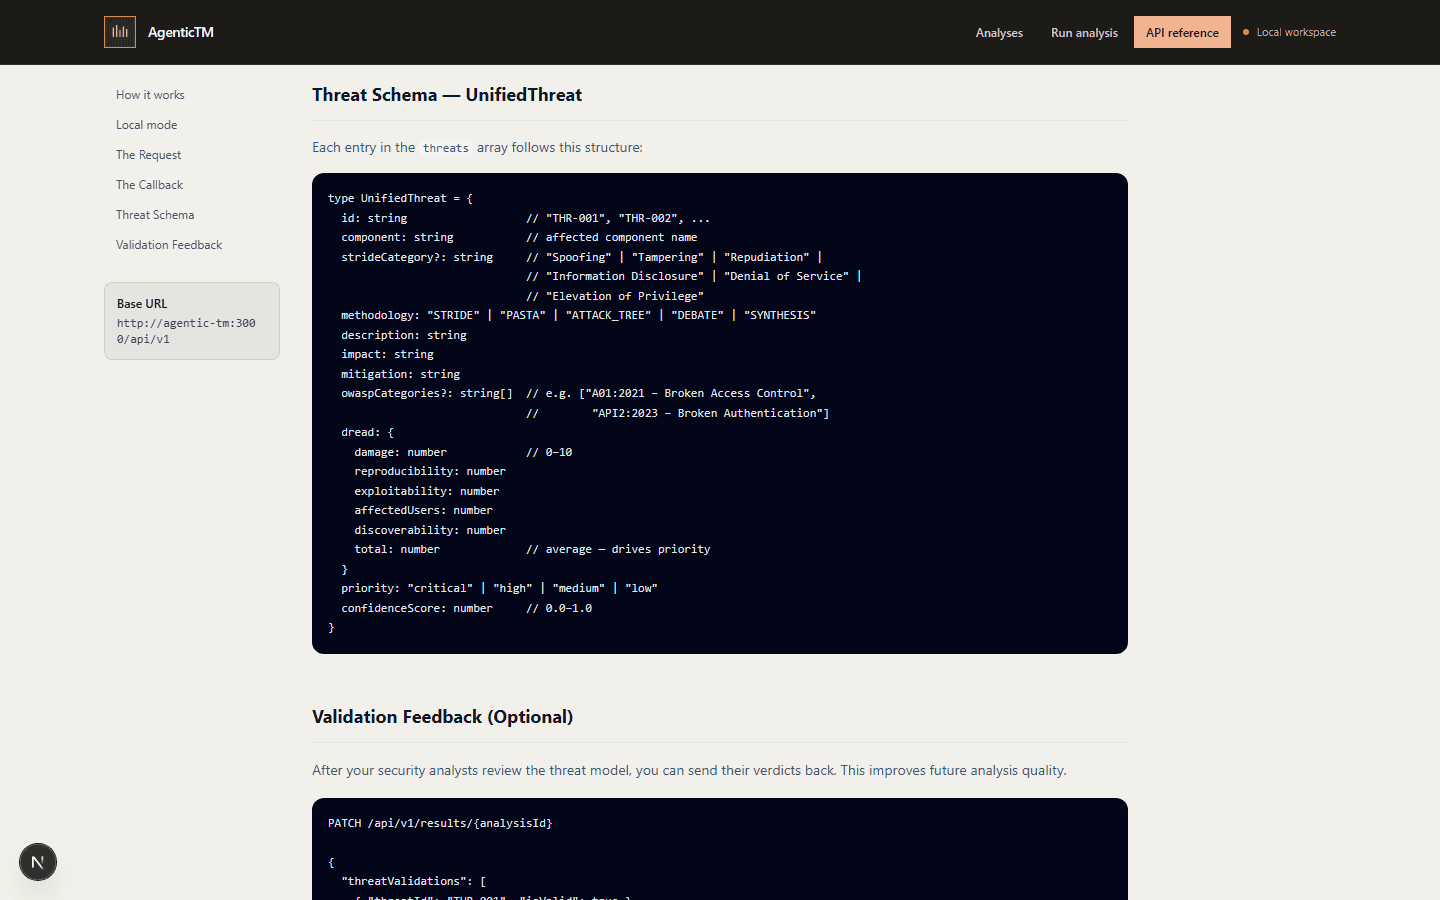
01/04
Threat model register
The workspace: completed analyses, live pipeline work, and the next decision in one place.
Waitlist
Get notified when it ships
Leave your email and you will be the first to know when Threat modeling, done by a pipeline of specialist agents. launches. One email when it ships, no spam.
The tool is coming. The method already works.
Nothing here has to wait for a release. The field guide carries the same method, and the assessment shows where to apply it first.
Back to the AI Security Lab